An ordinary trip should not require a privacy strategy. Neither should visiting a doctor, attending a religious service, or meeting people whose politics differ from the government’s.
Yet the direction of American privacy policy increasingly forces an uncomfortable question: how much of everyday life can become searchable before freedom itself begins to change?
The danger is a system assembled piece by piece. Companies collect information. Brokers package it. Government agencies acquire access. Each participant can describe a limited purpose while the combined system gains an extraordinary view of people’s lives.
Recent developments show why that deserves public resistance.
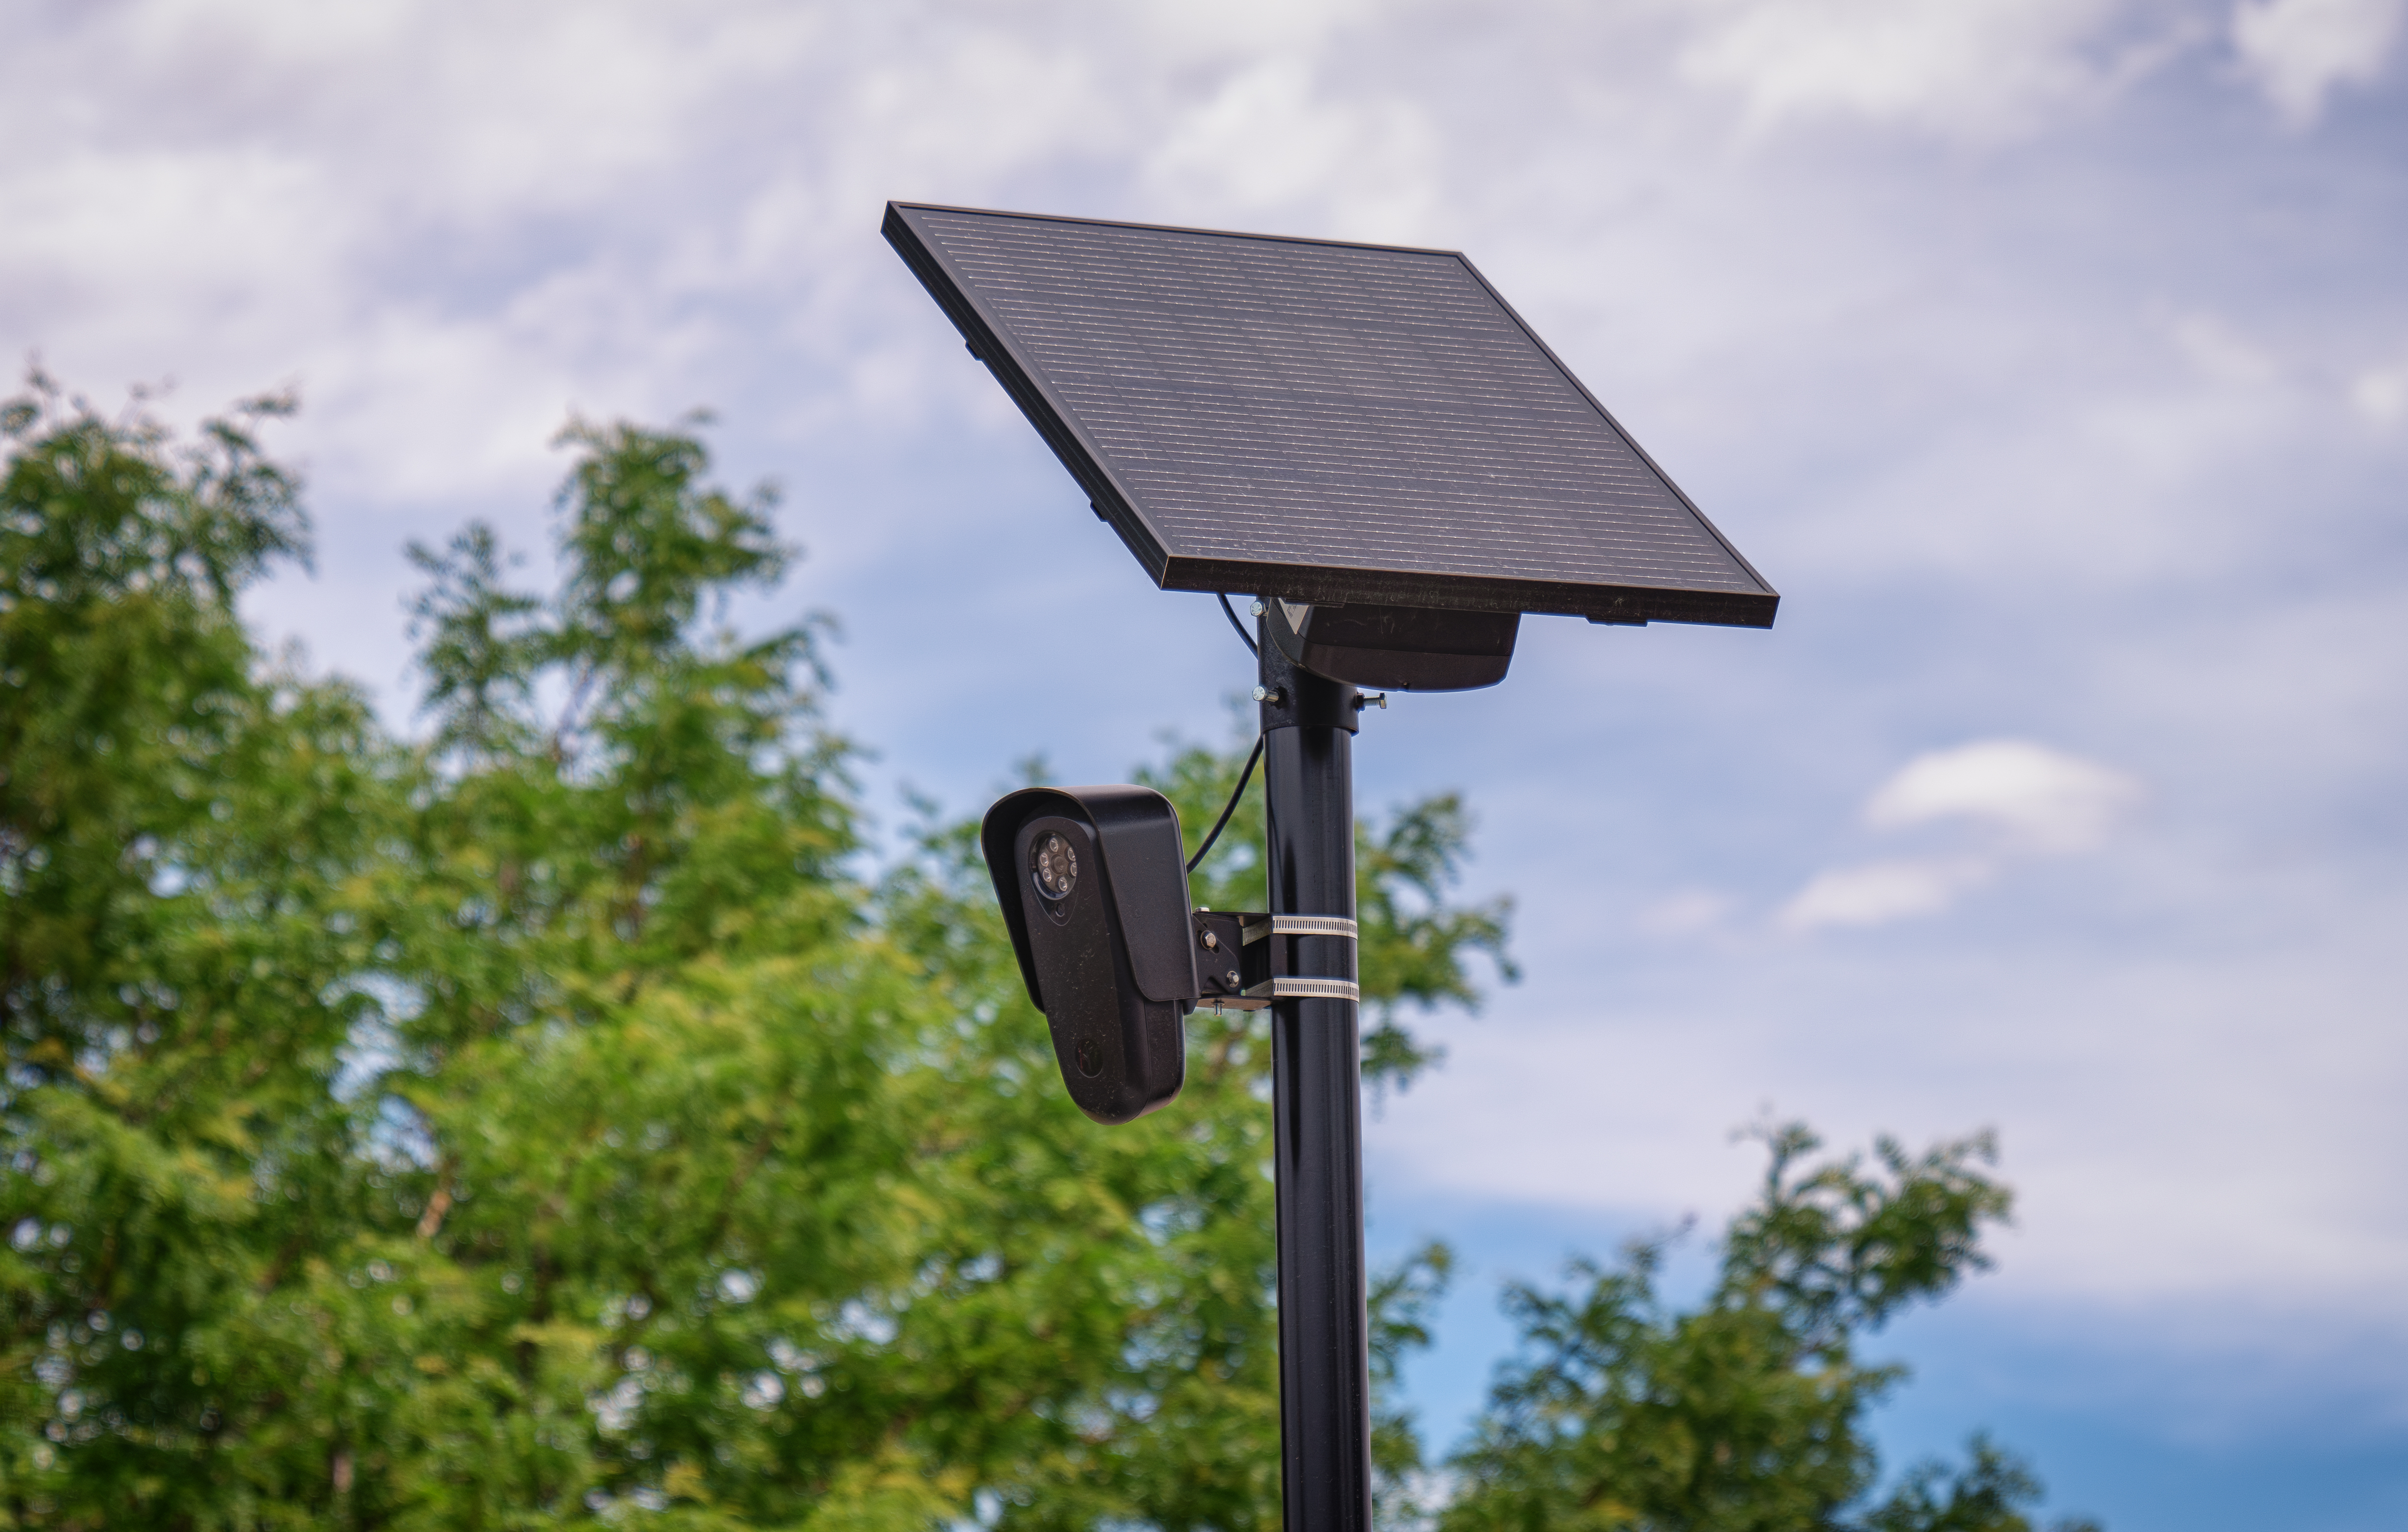
On September 17, Senators Ron Wyden and Adam Schiff announced an inquiry into alleged misuse of Flock’s surveillance systems, asking whether its safeguards adequately protect Americans. Their inquiry concerns reports of unauthorized searches involving a network of license plate readers and other sensors. These are allegations and questions under scrutiny, not a final judicial finding against the company. But they expose an essential policy problem: building a powerful tracking system also creates opportunities to misuse it. Source: senators’ announcement.
A vehicle passing a camera is one observation. A searchable history of its movements can reveal routines and associations. The privacy stakes change when scattered observations become a record someone else can examine.
That distinction should guide the rules before a system expands.
The commercial data market raises a similar problem. In December 2024, the Federal Trade Commission alleged that Gravy Analytics and its subsidiary Venntel collected and used location information without obtaining verifiable consent for commercial and government uses. The complaint also alleged that location data was used to derive sensitive characteristics involving health, political activity, and religion. Source: FTC complaint announcement.
A location record can carry meaning far beyond coordinates. A pattern of visits may suggest something deeply personal, and that inference may be wrong. Either possibility creates a problem for the person being categorized.
Government interest in commercial information is openly acknowledged. The intelligence community’s published framework describes its use of commercially available information, recognizes the risk of exposing sensitive personal details, and establishes baseline safeguards. That acknowledgment matters: the connection between commercial collection and government access is part of documented policy. Source: intelligence community framework.
Our position is that sensitive information should receive strong protection regardless of whether an agency obtains it from a company or collects it directly. A purchase should not reduce the scrutiny that intrusive access deserves.
The consequences extend beyond an embarrassing advertisement or an unwanted sales call. A searchable personal history can give institutions leverage over people who have little ability to inspect the record, challenge an inference, or learn who accessed it.
Consider a worker thinking about organizing colleagues, a person seeking sensitive medical care, or a resident considering a lawful protest. If they reasonably fear that their movements could be reconstructed later, they may decide the activity is too risky. That is the democratic danger: surveillance can discourage participation without anyone issuing an explicit prohibition.
Collecting sensitive information also creates security risks. On September 4, Wyden and Representative Pat Harrigan requested an investigation into how commercial location information about military personnel remained available despite protective measures. Their announcement described concerns about adversaries using such information to track American servicemembers. Source: bipartisan investigation request.
A market that exposes intimate information cannot reliably reserve its benefits for trustworthy buyers.
There are meaningful efforts to push back. California’s Delete Request and Opt-out Platform, DROP, lets eligible residents submit one deletion request to registered data brokers. Brokers were required to begin accessing the system to process requests starting August 1, 2026. This is a concrete improvement, although processing takes time and the service is limited to California residents. Source: California’s DROP guidance.
Its existence also highlights the burden placed on individuals. People should not have to become investigators of the data industry to regain control over their own information.
A better direction would start with collecting less. Sensitive data should have narrow permitted uses, short retention periods, and enforceable restrictions on sale and disclosure. Intrusive government access should face meaningful independent scrutiny. Surveillance systems should have auditable access controls, consequences for misuse, and a practical way for affected people to challenge errors.
Public safety is a legitimate responsibility. Agencies should demonstrate that a surveillance tool is necessary and proportionate, and that less intrusive approaches would not adequately serve the same purpose. Convenience alone is an inadequate justification for retaining everyone’s movements.
America’s privacy future remains a choice. We can keep expanding the record of ordinary life and hope each future user behaves responsibly. Or we can place enforceable limits on what gets collected and who can use it.
At Patch the State, we favor the limits.
A free society needs room for people to live without continually explaining themselves to whoever gains access next.